
Introduction to Encryption
To understand what is encryption, think of it as a way to conceal the meaning of digital information from unauthorized readers. It uses mathematical techniques to transform readable data into an unreadable form.
Encryption is relevant whenever sensitive information is stored on a digital system or transmitted between systems. It supports confidentiality and privacy, but its effectiveness depends on suitable cryptographic methods, correct implementation, and proper management.
What Is Encryption?
Encryption uses a cryptographic algorithm and a key to transform readable information, called plaintext, into an unreadable form called ciphertext. The purpose is to prevent unauthorized people from reading or using the original information.
When the encryption is reversible, an authorized process can use decryption to restore the ciphertext to its original form. Encryption and decryption therefore perform opposite parts of the protective process.
Why Encryption Matters
Encryption supports confidentiality by concealing information from people who are not authorized to read it. This can help protect privacy when digital systems handle sensitive records, communications, and transactions.
Data may require protection in two broad situations:
- Data at rest: Information stored on a device or another digital system.
- Data in transit: Information being exchanged or transmitted between systems.
Encryption can protect sensitive digital data in both situations when it is implemented and managed properly. Cryptographic methods also help secure digital exchanges such as e-commerce transactions and mobile communications.
How Encryption Works
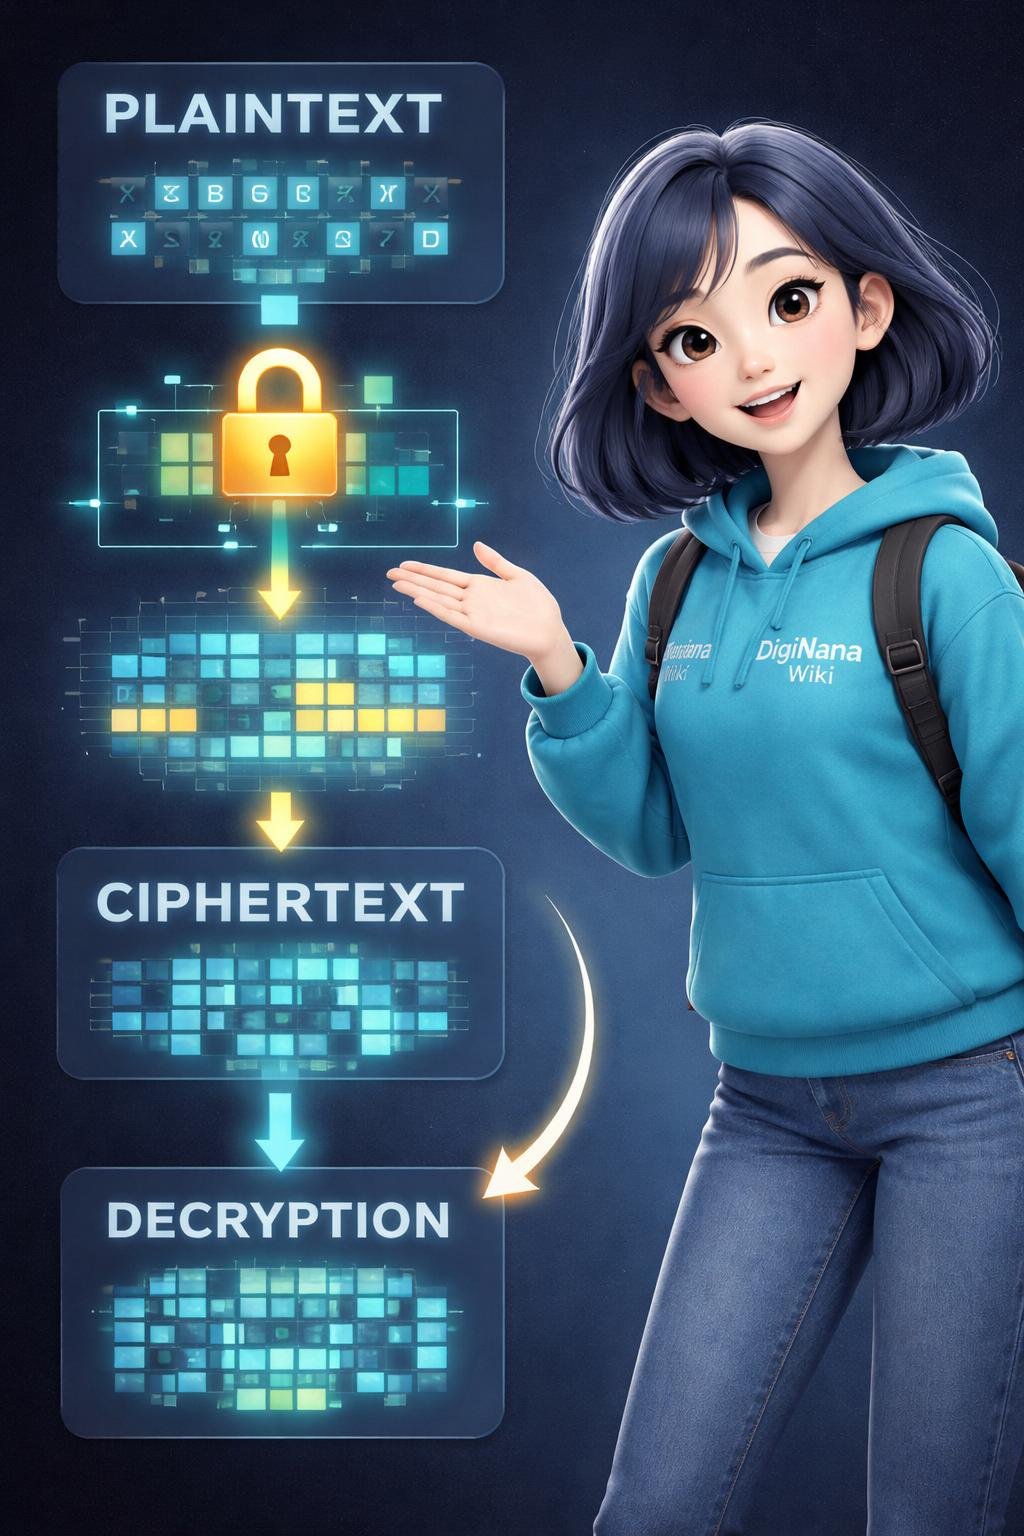
The basic encryption process has several steps:
- Information begins as readable plaintext.
- A cryptographic algorithm processes that plaintext.
- A key is used as part of the algorithm’s operation.
- The process produces ciphertext that conceals the original meaning.
- When authorized access is required, decryption restores the original information.
A key is an essential input to this process. The algorithm and key work together, so protecting and properly managing required keys is an important part of an encryption solution.
Key Components of Encryption
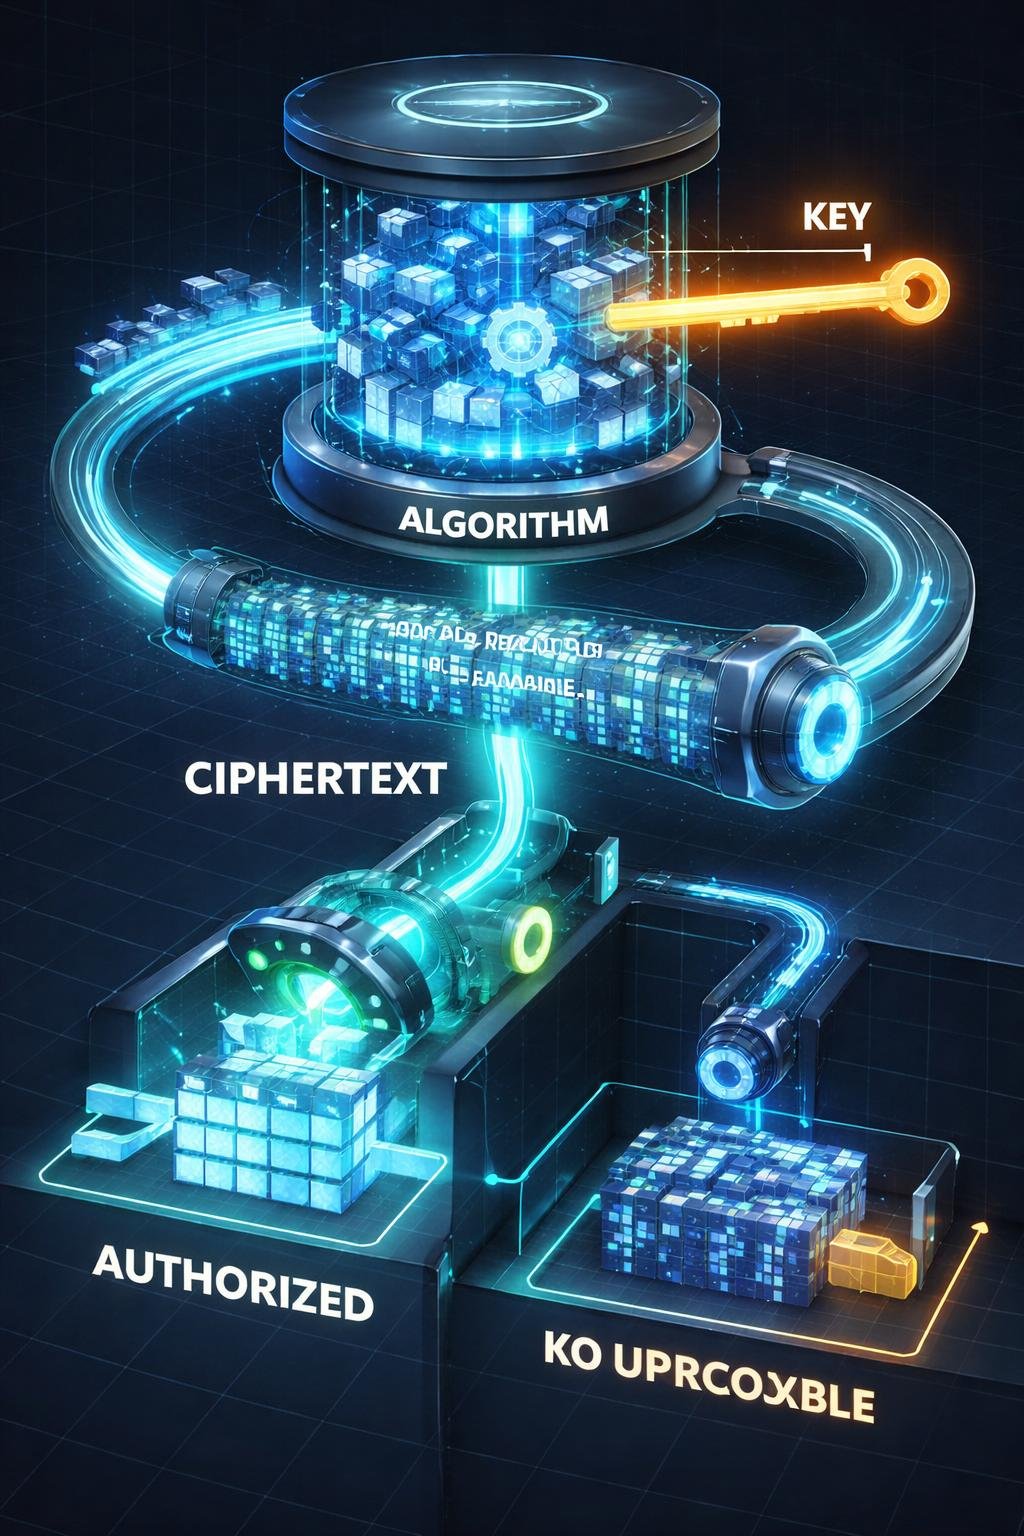
| Component | Meaning |
|---|---|
| Plaintext | The readable data before it is encrypted. Despite its name, plaintext can represent different kinds of digital information rather than only written text. |
| Ciphertext | The transformed form that conceals the original meaning of the data. |
| Cryptographic algorithm | The mathematical process used with a key to transform plaintext into ciphertext. |
| Key | An input used by the cryptographic algorithm during encryption or decryption. |
| Encryption | The process that changes plaintext into ciphertext. |
| Decryption | The authorized process that restores reversible ciphertext to its original state. |
| Key management | The part of an encryption solution concerned with properly handling and controlling its keys. |
Related Cryptographic Tools
Encryption is part of the broader field of cryptography, but not every cryptographic tool performs encryption.
- Cryptographic hash functions create short digests used in security applications. Hashing should not be treated as another name for reversible encryption.
- Digital signatures can provide assurance about the signer and whether information was modified after signing. Their role is different from concealing readable data.
- Message authentication codes are another category of cryptographic mechanism. They are documented separately from encryption and should not be assumed to perform the same function.
These mechanisms may appear within broader security systems, but their purposes must remain distinct.
Everyday Examples of Encryption
Example: E-commerce transactions. Cryptographic methods can help secure the exchange of data involved in digital commerce. This illustrates protection for information while it is being exchanged.
Example: Mobile communications. Encryption methods can be used as part of protecting data exchanges in mobile communications.
Example: Sensitive patient information. Encryption can protect sensitive digital records while they are stored and while they are transmitted. The effectiveness of that protection still depends on how the encryption solution is implemented and managed.
These examples describe general uses identified in the verified sources. They do not claim that every service, device, transaction, or record system uses the same encryption configuration.
Benefits and Limitations of Encryption
Benefits
- It conceals the original meaning of digital data from unauthorized readers.
- It supports confidentiality and privacy.
- It can protect sensitive information while stored and while in transit.
- It can support secure digital data exchanges.
Limitations
Encryption is not effective merely because it is present. Protection also depends on understanding the security properties being provided, selecting suitable cryptographic standards and methods, implementing the solution properly, and managing it correctly.
Encryption specifically addresses the confidentiality of data. It does not make every part of an account, device, service, or recovery process secure, and no encryption method should be presented as a guarantee of complete protection.
Common Misunderstandings About Encryption
“Encryption and hashing are the same.”
They are not interchangeable. Encryption transforms plaintext into ciphertext and may be reversed through authorized decryption. A cryptographic hash function creates a digest for use in security applications.
“Digital signatures are another type of encryption.”
Digital signatures have a different purpose. They can provide assurance about the signer and whether signed information was changed after signing, while encryption is used to conceal the meaning of data.
“Ciphertext can never be restored.”
Reversible encryption is designed so that authorized decryption can restore the encrypted information to its original state.
“Encryption guarantees complete security.”
Encryption protects confidentiality, but effective protection also requires proper implementation, management, and use of suitable cryptographic methods. Other account, device, and recovery risks still require attention.
DigiNana Beginner Guide
Fictional educational example: DigiNana writes a readable note for an authorized recipient. In the example, the note represents plaintext.
DigiNana explains that a cryptographic algorithm processes the note with a key. The result is ciphertext, which does not reveal the note’s original meaning to an unauthorized reader. When the authorized recipient needs the note, an authorized decryption process restores the readable information.
This story is a conceptual illustration, not a real product test or a description of a particular software interface. The verified technical principle is that encryption uses an algorithm and key to transform plaintext into ciphertext, while reversible encryption allows authorized decryption to restore the original data.
Practical Tips
- Use encryption solutions that are properly implemented and managed rather than assuming that any encryption label is sufficient.
- Consult current official documentation to understand what information a system protects and whether that protection applies to stored data, transmitted data, or both.
- Protect access to encrypted information as well as the encryption itself.
- Do not share passwords, recovery codes, private keys, or other confidential access information.
- Follow the official recovery process for the relevant service or system, and do not give secrets to someone who requests them unexpectedly.
- Review important security information when software, services, or devices change because features and recommended protections may also change.
These steps support safer use, but they do not make any system completely secure.
Encryption, Safety, and Privacy
Encryption is one part of broader data and account protection. It can conceal stored or transmitted information, but users must still remain alert to phishing, malware, unauthorized access, and unsafe recovery practices.
A deceptive message may try to persuade a person to reveal a password, recovery code, private key, or other secret. Encryption does not prevent someone from voluntarily disclosing confidential access information, so unexpected requests for secrets should be treated cautiously and checked through an official channel.
Malware or unauthorized account access can create risks outside the narrow confidentiality protection supplied by encryption. Account controls, device protection, careful handling of secrets, and safe recovery practices therefore remain relevant.
If access may have been compromised, use the current official support and recovery documentation for the affected service or system. Never send passwords, authentication codes, recovery codes, or private keys to an unverified person.
Frequently Asked Questions
What are plaintext and ciphertext?
Plaintext is readable information before encryption. Ciphertext is the transformed output that conceals the original meaning.
What is the difference between encryption and decryption?
Encryption transforms plaintext into ciphertext by using a cryptographic algorithm and key. Authorized decryption restores reversible ciphertext to its original form.
Can encryption protect both stored and transmitted data?
Yes. Encryption can protect sensitive digital information while it is stored and while it is in transit, provided the encryption solution is properly implemented and managed for the relevant situation.
Why are keys important?
A key is an input used with a cryptographic algorithm. Proper key handling and management are therefore essential parts of an effective encryption solution.
Is hashing the same as encryption?
No. Encryption produces ciphertext and may support authorized reversal through decryption. Cryptographic hashing creates a short digest used in security applications and should not be treated as reversible encryption.
Does encryption guarantee complete protection?
No. Encryption supports confidentiality, but it does not remove every risk. Proper implementation, management, account protection, phishing awareness, malware prevention, and safe recovery practices remain important.
Final Takeaway
Encryption uses mathematical techniques, cryptographic algorithms, and keys to transform readable plaintext into ciphertext that conceals the data’s original meaning. With reversible encryption, authorized decryption can restore the original information.
Encryption can protect sensitive data while it is stored and while it is in transit. Its effectiveness depends on suitable cryptographic methods, proper implementation, careful management, and protection of confidential access information.
References
- Cryptography | NIST — https://www.nist.gov/cryptography
- Encryption Basics | NIST — https://www.nist.gov/publications/encryption-basics
- Cryptographic Standards and Guidelines | CSRC — https://csrc.nist.gov/Projects/cryptographic-standards-and-guidelines
- encryption – Glossary | CSRC — https://csrc.nist.gov/glossary/term/encryption
Image Credits
The five DigiNana Wiki visuals accompanying this article are original educational illustrations created with AI assistance. They are conceptual images and must not be interpreted as verified photographs, exact software interfaces, actual device specifications, or guaranteed technical configurations.
Disclaimer
This article provides general educational information. Security threats, technical information, software interfaces, product features, service availability, and recommended protective measures can change over time. Verify important details using current official documentation for the relevant technology or service. No encryption method or other security measure guarantees complete protection.